GCP Platform Operations
A Google Cloud setup for releasing software, investigating problems and reviewing running costs.
Built to deploy. Designed to operate.
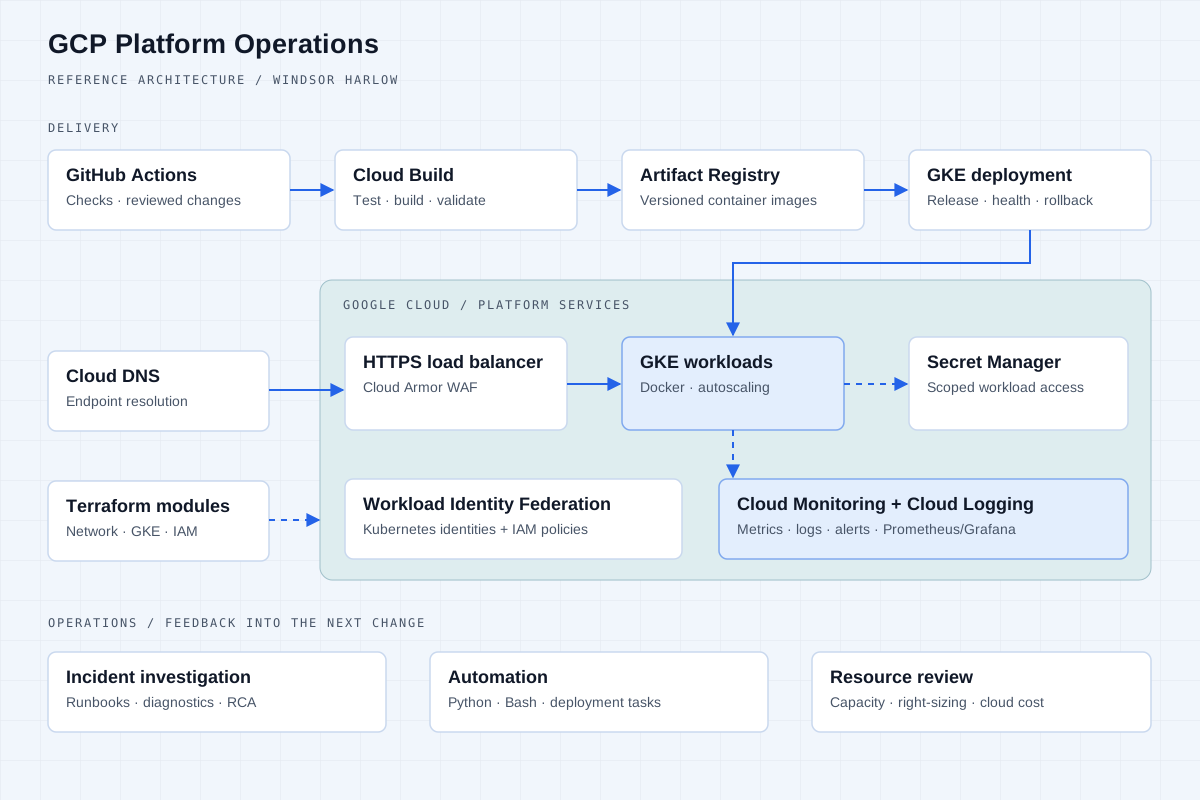
A Google Cloud platform built with reusable Terraform code and Google Kubernetes Engine (GKE). It combines automated releases with network controls, access management and tools for monitoring and troubleshooting.
Decisions that shape the system.
A repeatable foundation
Reusable Terraform modules define VPCs, subnetworks, routing, firewall rules, IAM and GKE, kept in version control and reviewed.
A controlled delivery path
GitHub Actions and Cloud Build automate checks, builds and deployments; Workload Identity, scoped IAM and Secret Manager connect workloads safely.
Operations as part of the platform
Monitoring, logs and alerts link to incident runbooks; Python and Bash automation support diagnostics and cost reviews.
What it does.
Reusable Terraform
Modules for the platform foundation.
Network controls
VPC, firewalls, DNS and Cloud Armor.
Deployment automation
GitHub Actions and Cloud Build.
Workload identity
Scoped IAM and managed secrets.
Operational visibility
Metrics, logs, alerts and runbooks.
Cost awareness
Usage reviews and right-sizing.
Built with.
Engineering lab — an independent reference build, not client work. The diagram is a reference view of the platform.
AWS Infrastructure as Code